How to let all data go through VPN?
If you want all network traffic on the router to be routed through the VPN, and block all Internet connections when the VPN fails, please follow the steps below to enable the VPN Kill Switch.
Note: Set up VPN client on your GL.iNet router first before enabling VPN Kill Switch.
For firmware v4.7 or earlier
Log in to your router's web Admin Panel, navigate to VPN -> VPN Dashboard -> VPN Client section, and click Global Options.
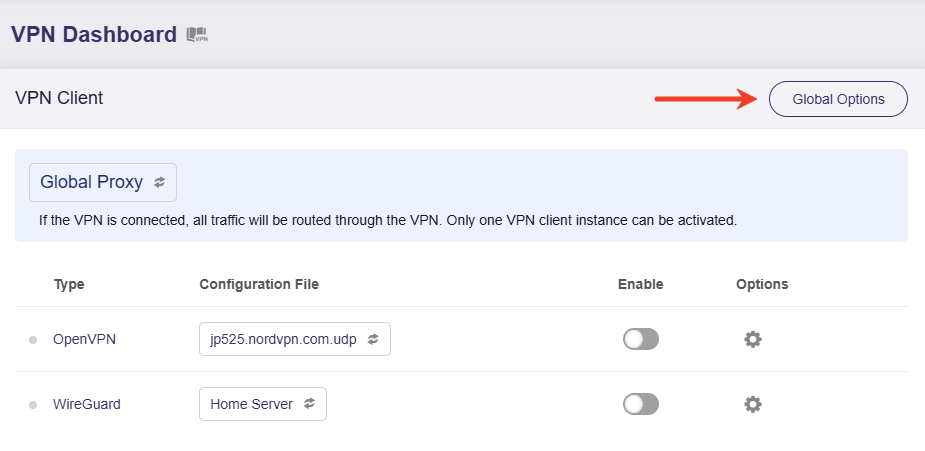
Toggle on Block Non-VPN Traffic (also called Kill Switch in some firmware version), then click Apply.
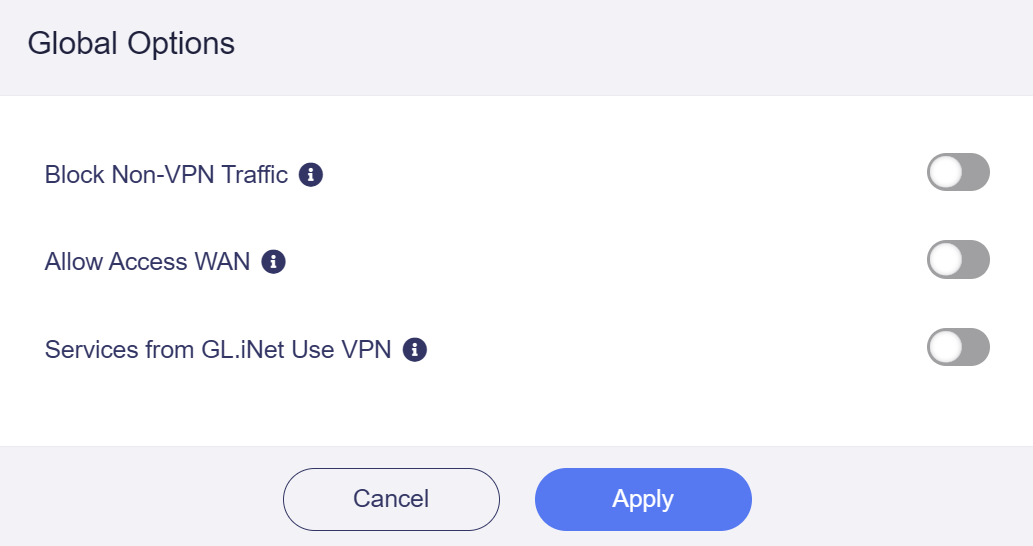
Note: When Block Non-VPN Traffic / Kill Switch is enabled, if your VPN is disabled or disconnected, all devices connected to the router will be restricted from accessing the Internet to prevent DNS leaks.
For firmware v4.8
In firmware v4.8, the VPN Kill Switch has been split into two modes.
-
Tunnel Kill Switch: It is enabled by default when the corresponding VPN tunnel is activated.
-
Enhanced Kill Switch (in Policy Mode): It is disabled by default to ensure that all traffic not covered by the VPN tunnels and policies above can still access the Internet. In short, it maintains normal Internet access for non-VPN traffic.
Tunnel Kill Switch
On the router's web Admin Panel, navigate to VPN -> VPN Dashboard.
If you set your router as a VPN client, the Kill Switch for this VPN tunnel is enabled by default once the VPN is activated.
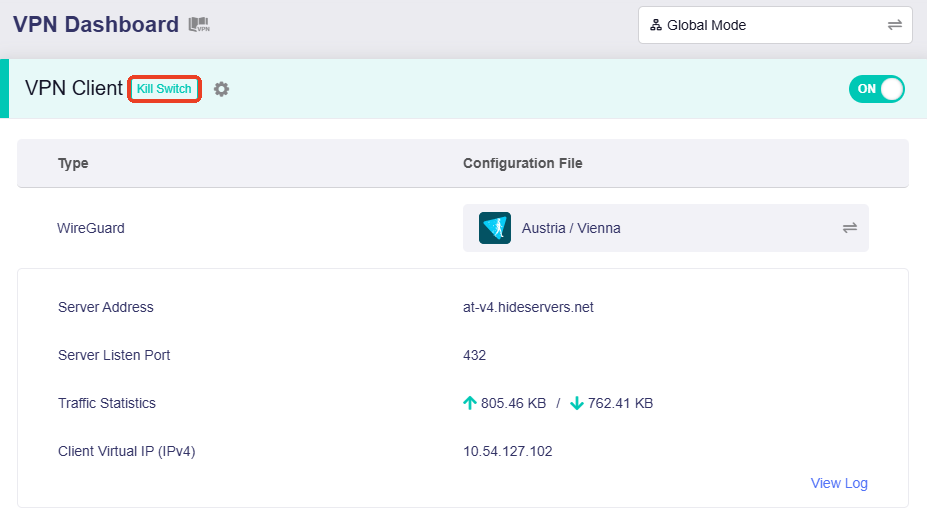 (VPN Global Mode)
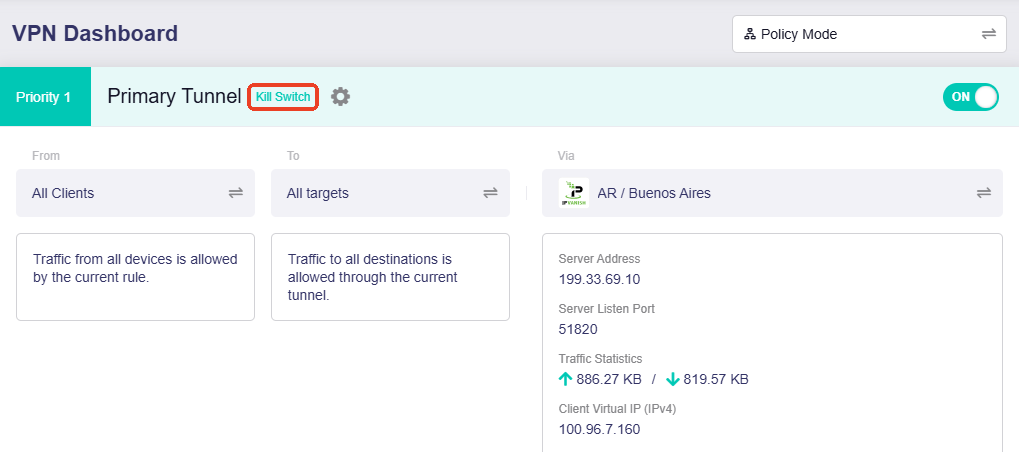 (VPN Policy Mode)
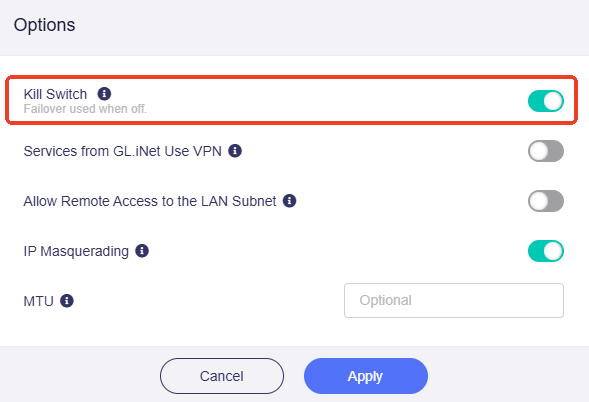
Click the gear icon next to the tunnel name to enter the Tunnel Options.
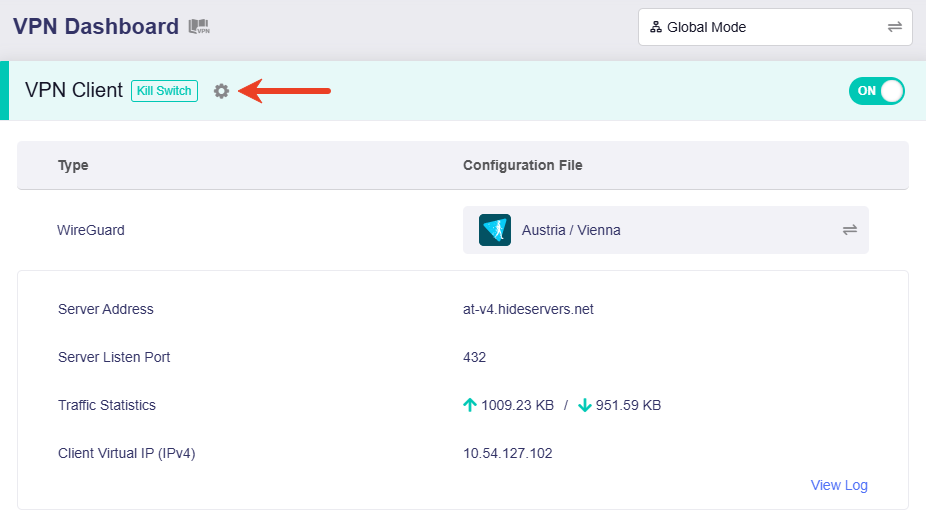
The Kill Switch for this tunnel is enabled by default.
Enhanced Kill Switch
This is available in Policy Mode.
On the router's web Admin Panel, navigate to VPN -> VPN Dashboard, switch the VPN mode to Policy Mode, then find a section named All Other Traffic at the bottom. This section may vary slightly depending on the firmware version.
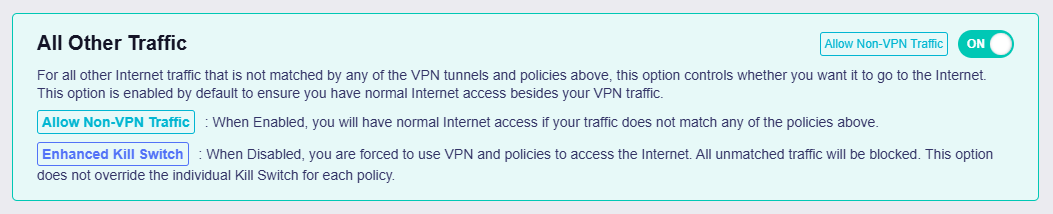
All Other Traffic serves as the default tunnel, ensuring normal Internet access for traffic that does not match any of the VPN tunnels or policies above, and for traffic rerouted here by VPN failover. It is enabled by default. Turning it off blocks all such traffic, including traffic that would otherwise fail over from a VPN connection, so only traffic handled by the configured VPN tunnels can reach the Internet — the same protection the Enhanced Kill Switch provides.
Note: The All Other Traffic setting does not override the individual Kill Switch for each tunnel.
For firmware v4.9 and above
In firmware v4.9 and above, two types of VPN Kill Switch are available: Tunnel Kill Switch and Enhanced Kill Switch.
Tunnel Kill Switch
On the router's web Admin Panel, navigate to VPN -> VPN Dashboard.
If you set your router as a VPN client, the Kill Switch for this VPN tunnel is enabled by default once the VPN is activated.
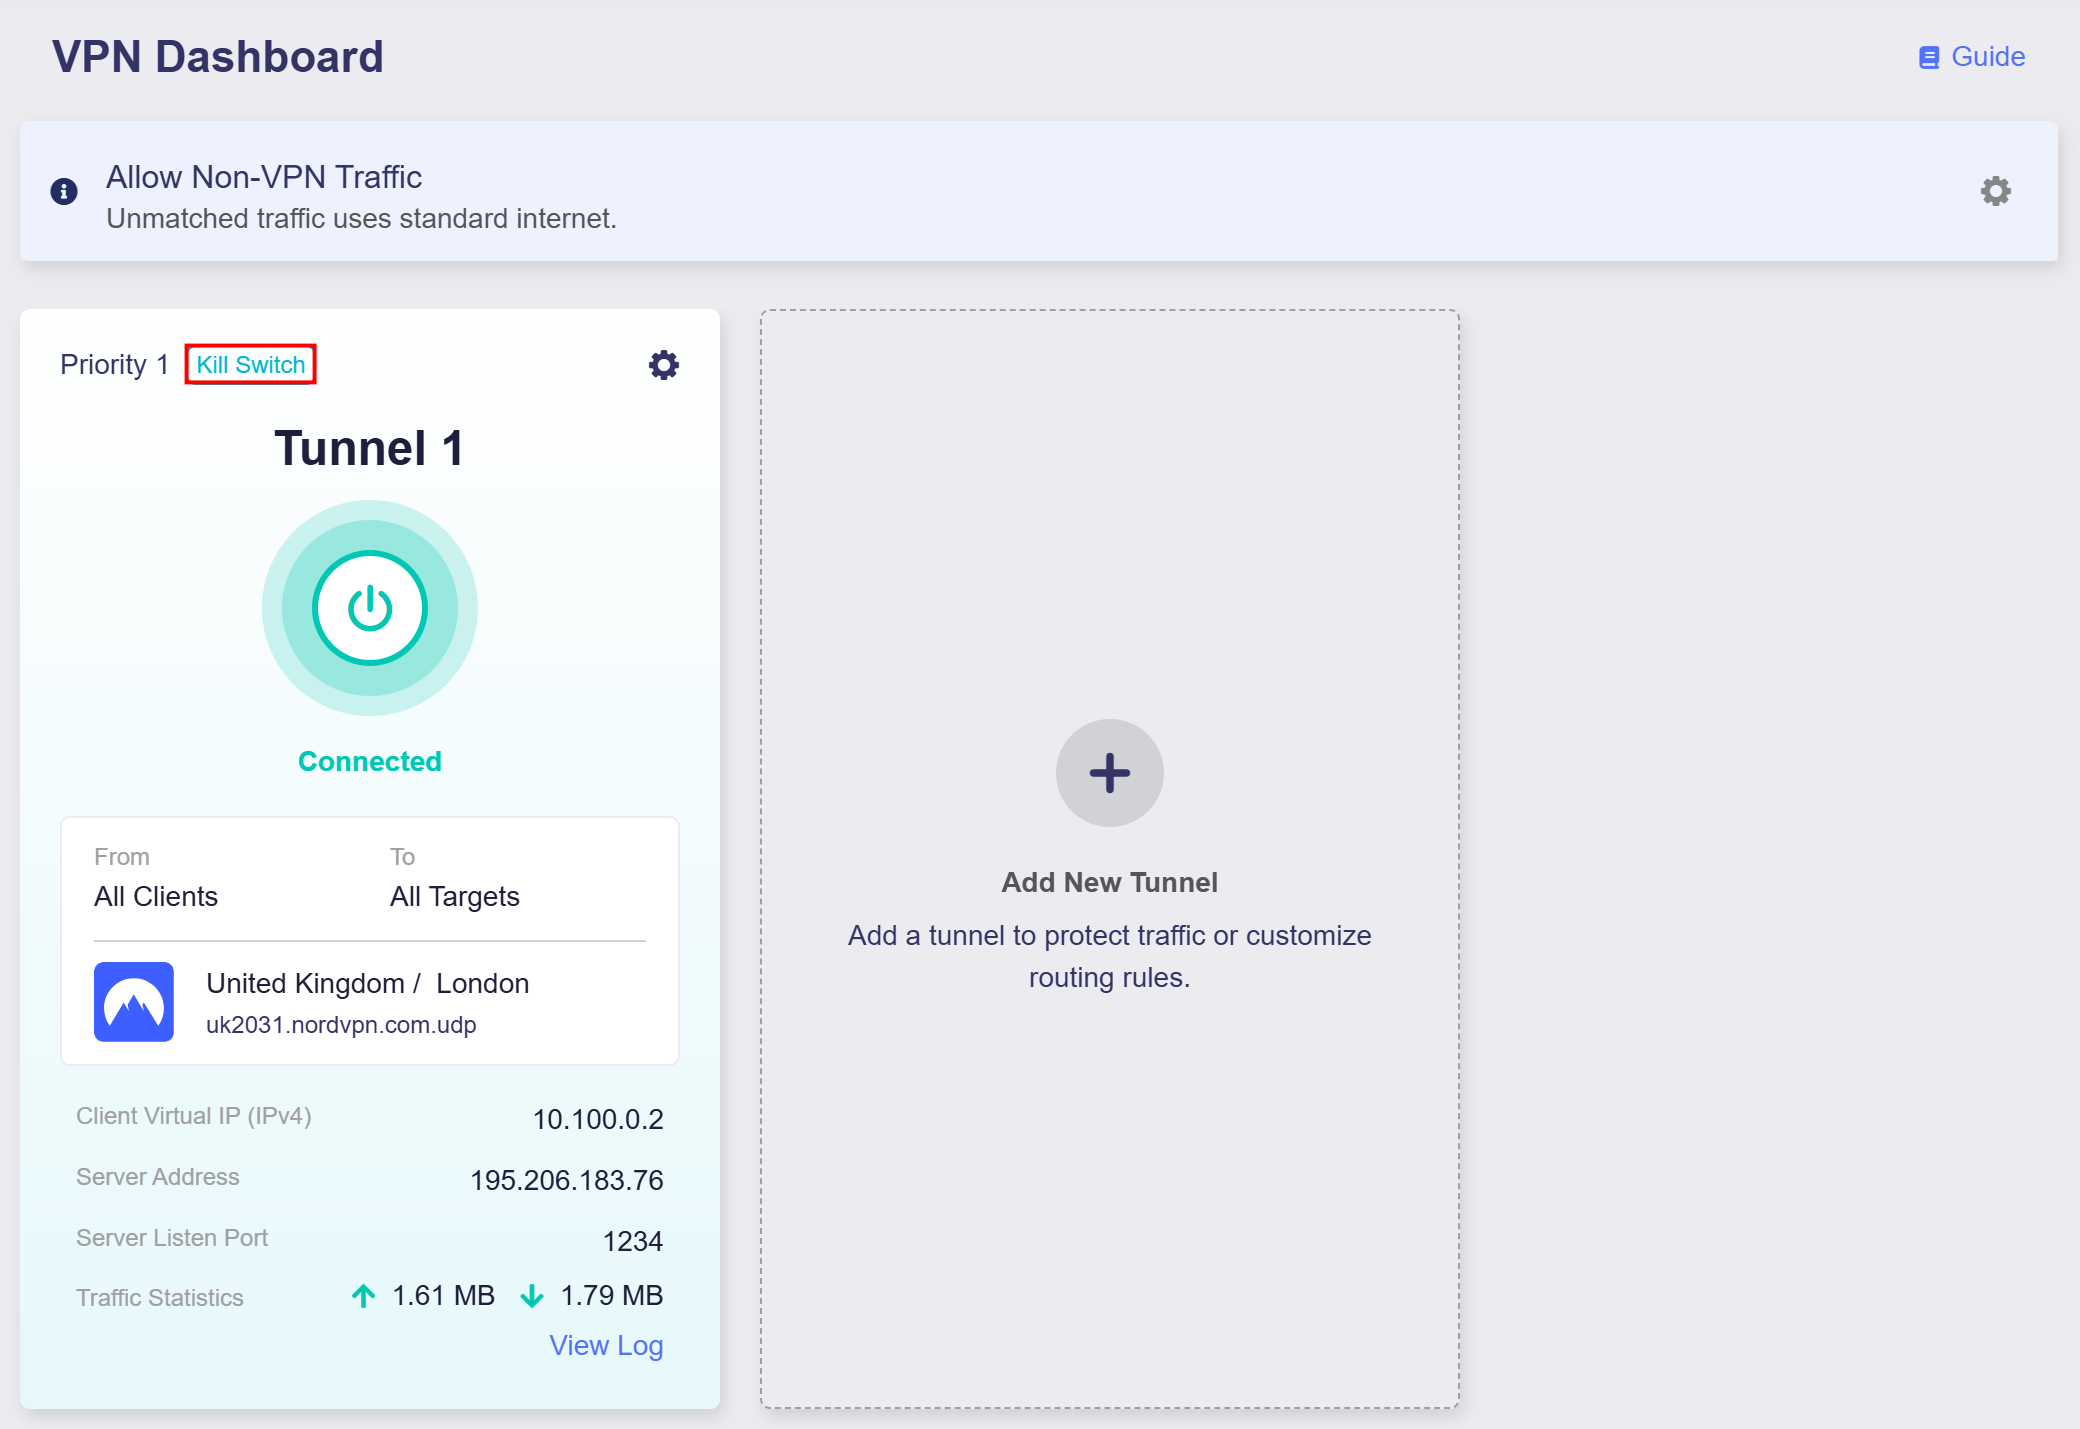
Click the gear icon next to the tunnel name to enter the Tunnel Options.
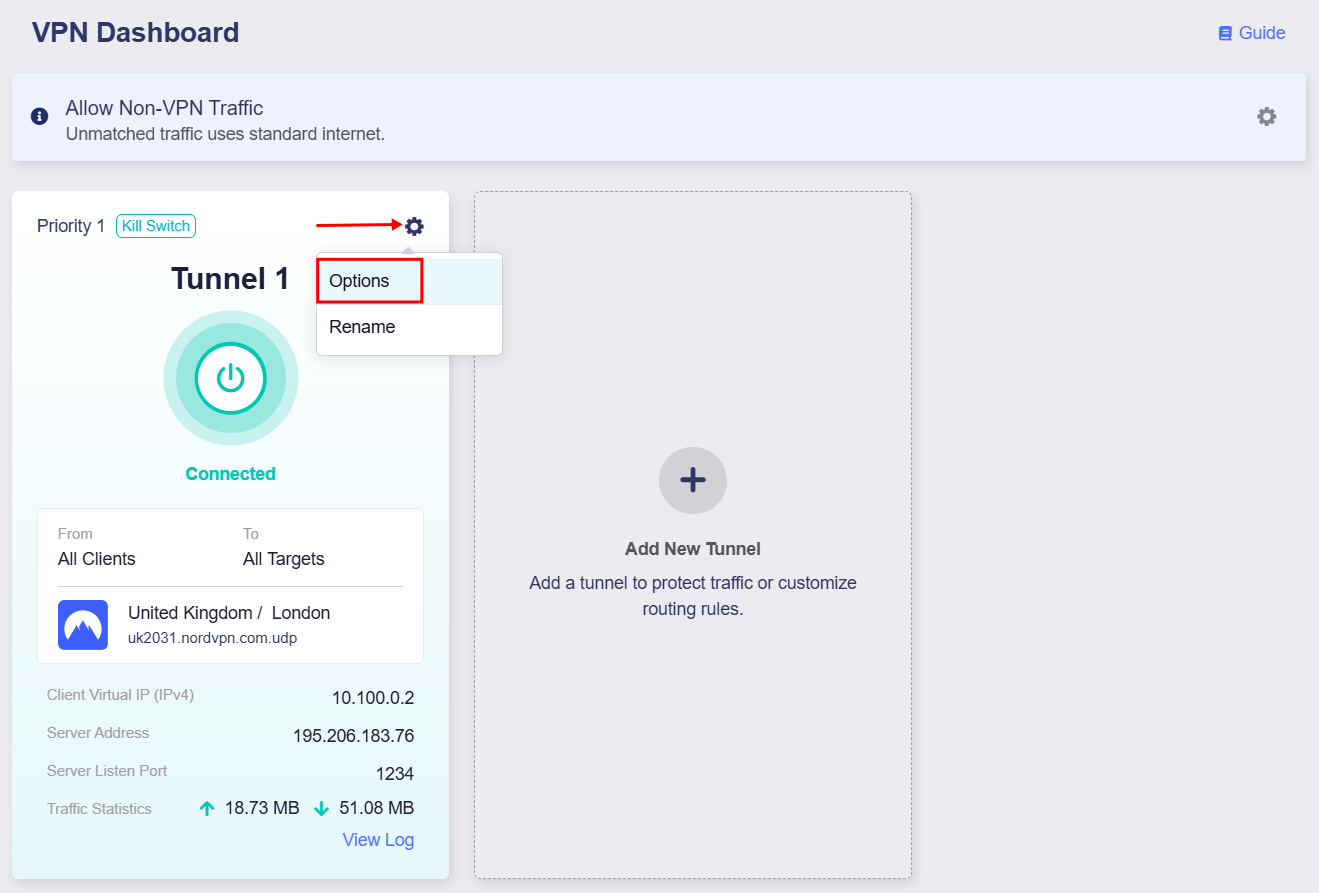
The Kill Switch for this tunnel is enabled by default.
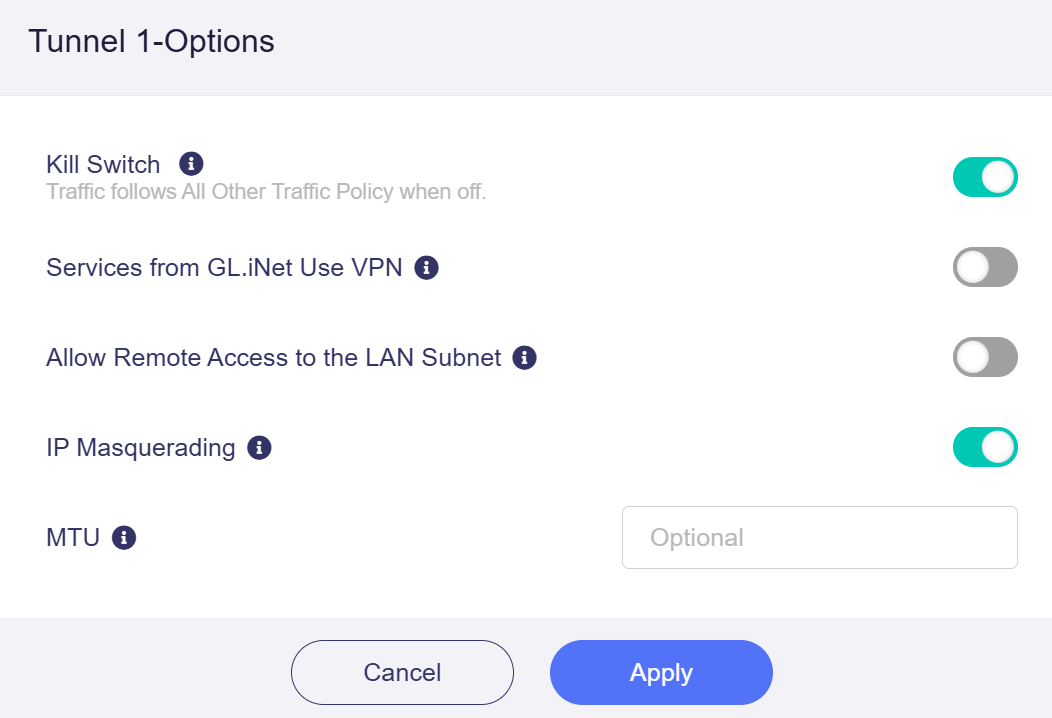
Enhanced Kill Switch
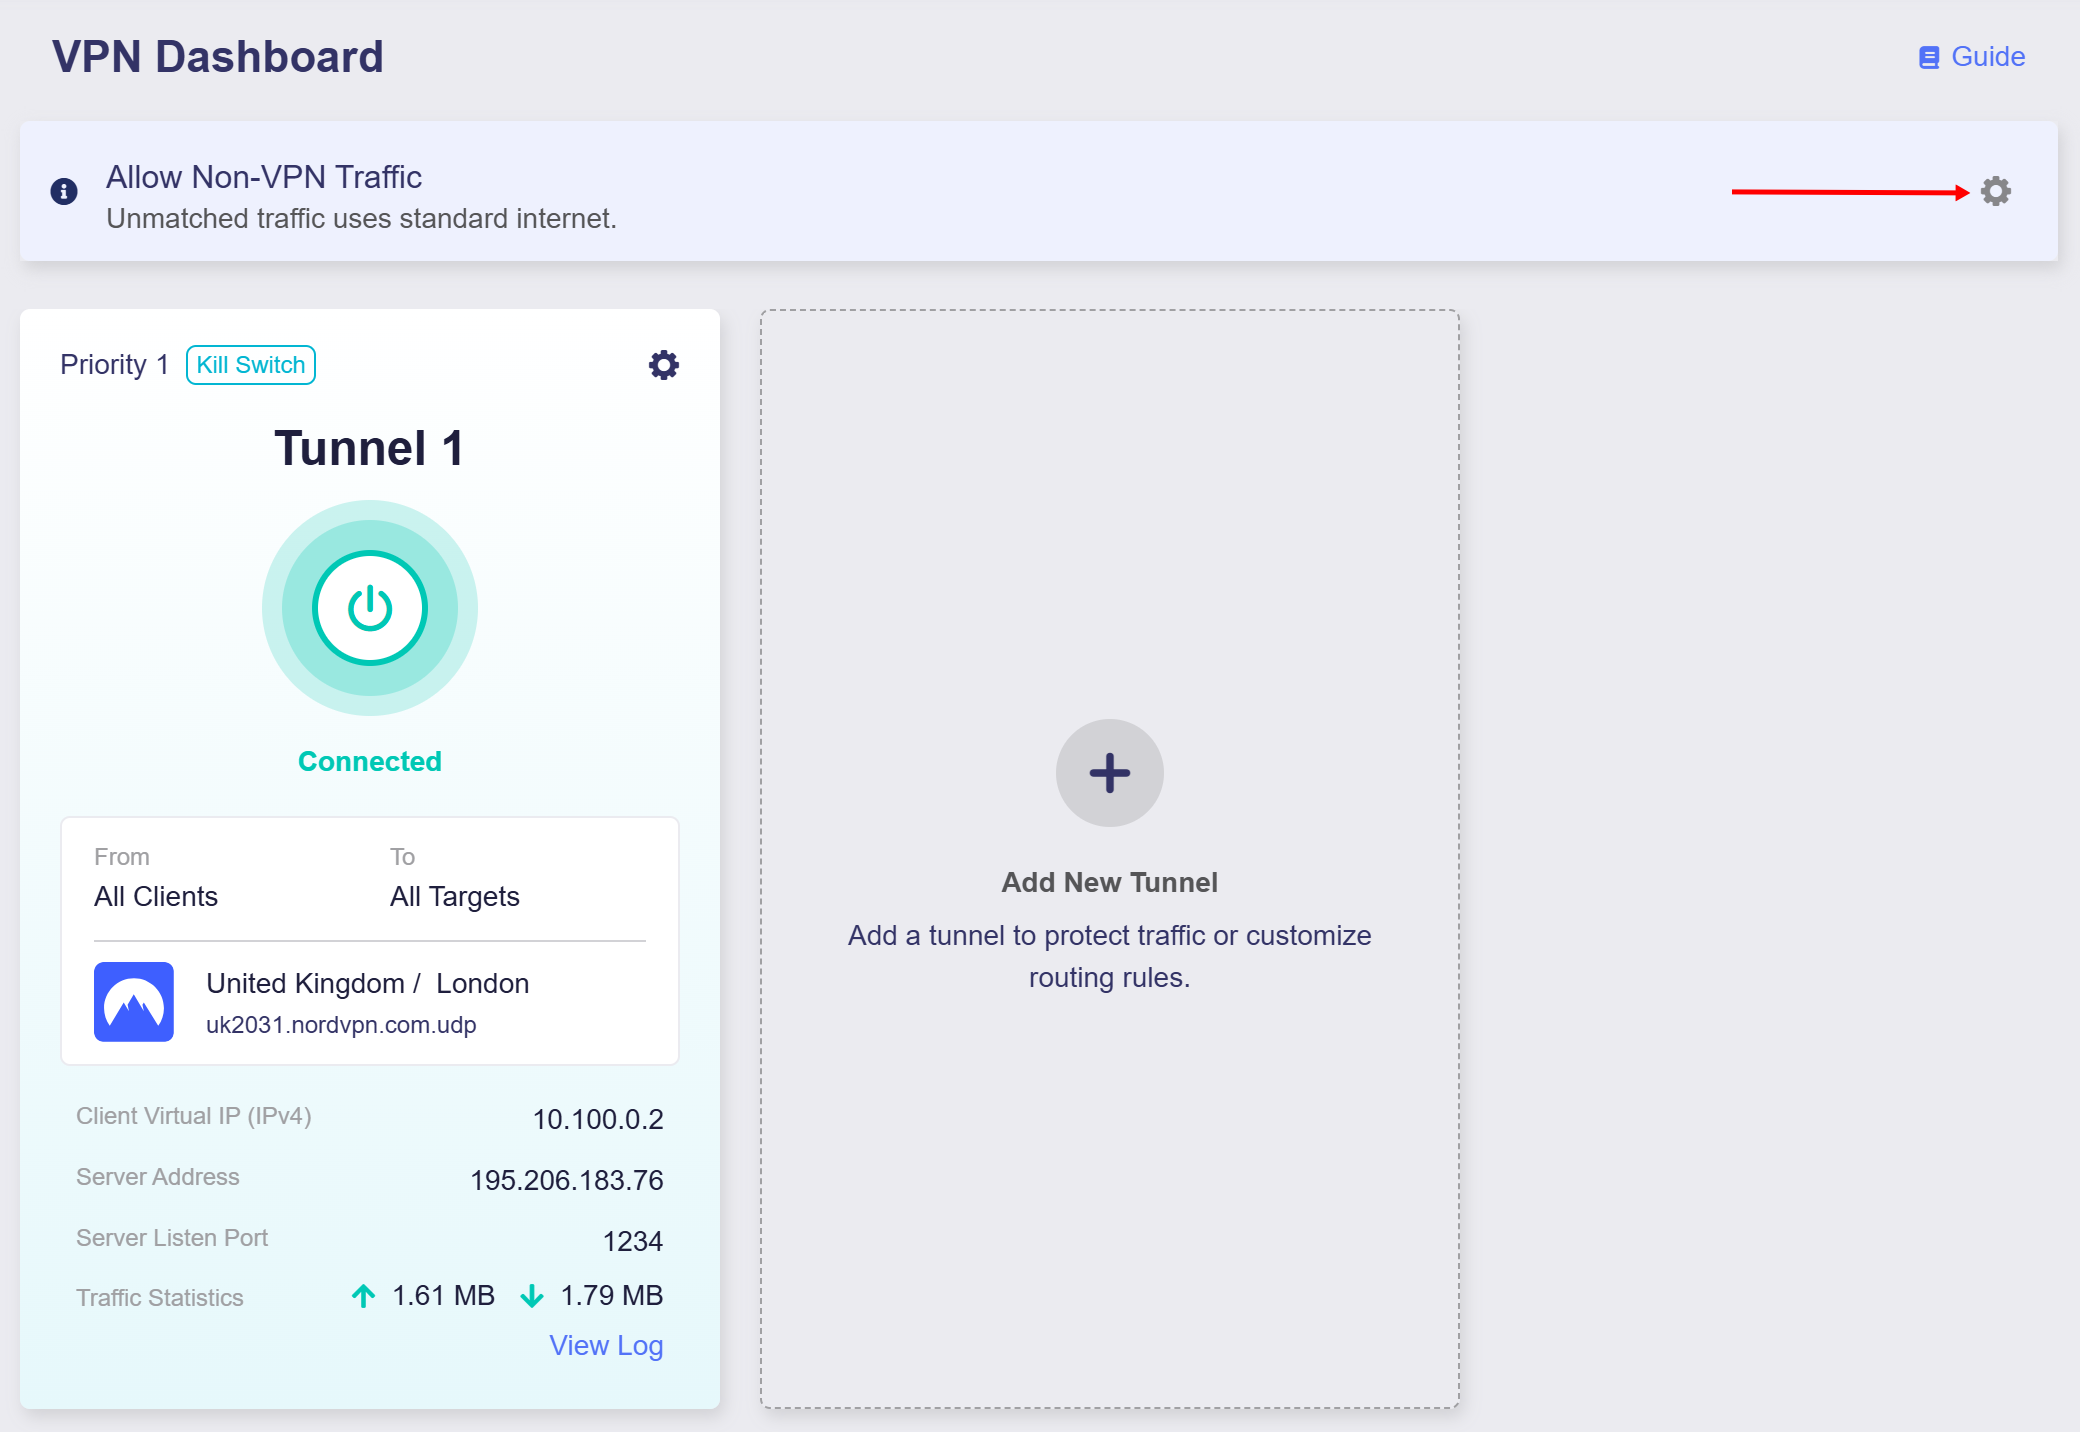
On the router's web Admin Panel, navigate to VPN -> VPN Dashboard, then click the gear icon in the upper-right corner.
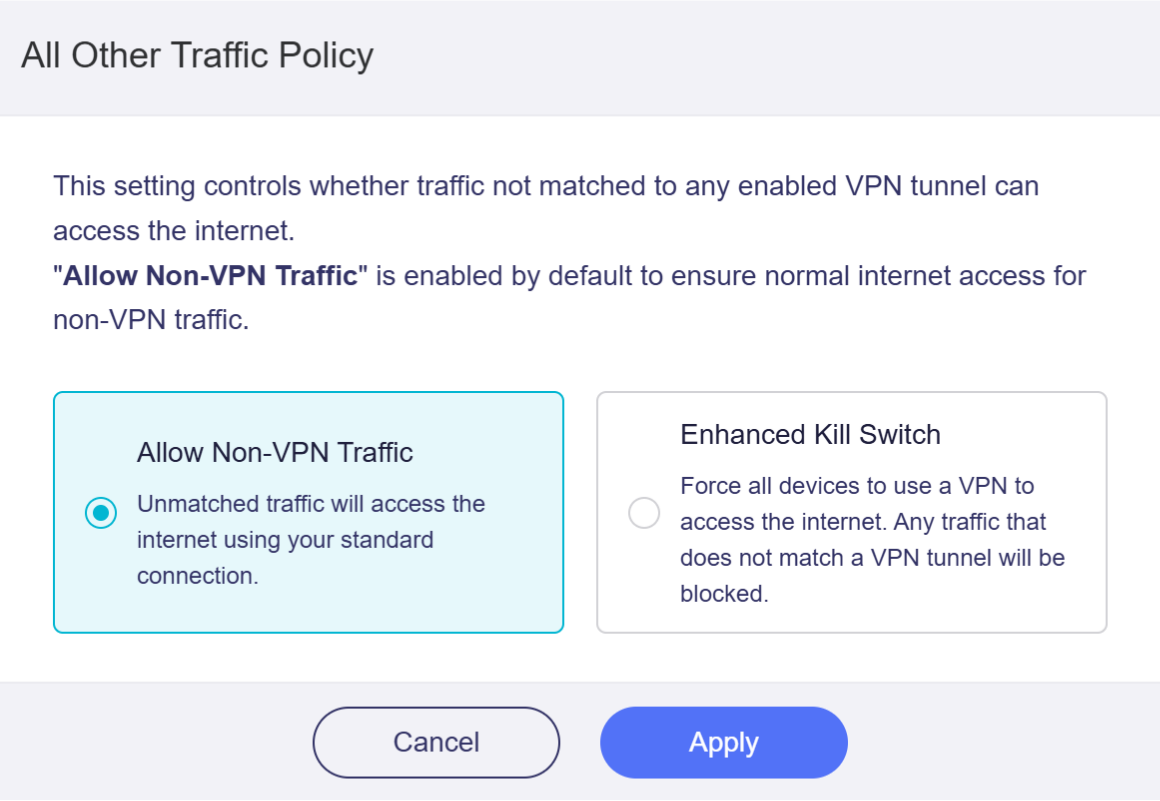
The traffic policy control provides two options: Allow Non-VPN Traffic and Enhanced Kill Switch.
-
Allow Non-VPN Traffic: Enabled by default. It allows normal Internet access for traffic that does not match any of the VPN tunnels or policies above, and for traffic rerouted here by VPN failover.
-
Enhanced Kill Switch: When enabled, it forces all devices to access the Internet through a VPN. Any traffic that does not match a VPN tunnel will be blocked. This setting does not override the Kill Switch configured for individual VPN tunnels.
Still have questions? Visit our Community Forum or Contact us.